Stay in control of AI across your whole company
Control all your data, connected tools, and agents.
Activity
All activity across all MCP servers
Last 24 hours
| Server | Time | Tool | User | Source | Latency | Status |
|---|---|---|---|---|---|---|
 | Mar 11, 2026 • 3:49 PM | Get Channel History | MM Teammate | — | 376ms | Success |
 | Mar 11, 2026 • 3:45 PM | List Projects | TB Teammate | — | 796ms | Success |
 | Mar 11, 2026 • 3:45 PM | Create Issue | MB Teammate | — | 651ms | Success |
| Mar 11, 2026 • 3:34 PM | Get Channel History | OG Teammate | — | 804ms | Success |
| Mar 11, 2026 • 3:25 PM | List Goals | AR Teammate | — | 394ms | Success |
 | Mar 11, 2026 • 3:22 PM | Base Schema | RB Teammate | — | 539ms | Error |
| Mar 11, 2026 • 3:11 PM | Get Channel History | AK Teammate | — | 226ms | Success |
 | Mar 11, 2026 • 3:07 PM | List Actors | BS Bella Shim | — | 384ms | Success |
 | Mar 11, 2026 • 3:00 PM | Update Event | LM Luis Manrique | — | 614ms | Error |
| Mar 11, 2026 • 2:55 PM | Search Users | AC Andreina Coronado | — | 373ms | Success |
| Mar 11, 2026 • 2:48 PM | List Channels | OG Teammate | — | 272ms | Success |
 | Mar 11, 2026 • 2:34 PM | Create Item | LM Luis Manrique | — | 763ms | Success |
Rows per page
Security and trust, built for the agentic era


Certifications and assessments

Privacy and how your data is used
We have zero data retention (ZDR) agreements with major large language model providers. You choose which models and providers your agents use, and you can bring your own keys (BYOK) so calls run through your own provider accounts.
Compliance and data handling
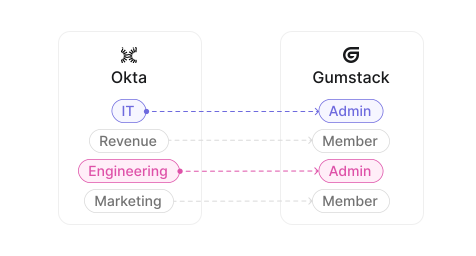
Access and infrastructure
Data is encrypted in transit and at rest. Connect any identity provider for single sign-on (SSO) and automated user provisioning with SCIM.

Deployment you control
Run Orchestrivo as managed SaaS, or deploy into your own cloud (VPC), in the region of your choice. Your data stays in the infrastructure you control.
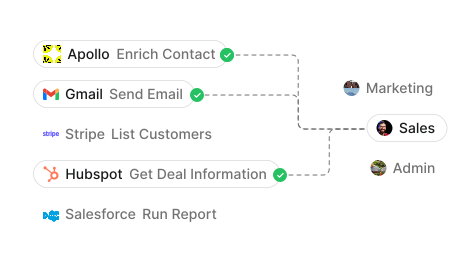

Governance for agents and MCP
Control what your agents and tools can do: role- and attribute-based access, per-tool authorization, full traceability for every tool call, and a live inventory of every MCP server in use. Secrets are managed centrally, and never sit in plaintext on someone’s laptop.
Deep governance for every agent and MCP server
Learn more about agent and MCP governance with Orchestrivo Controls.
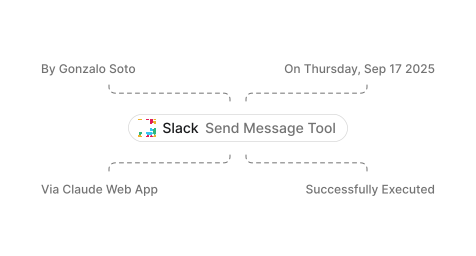
Tool call traceability
Every call is tied to a specific user, agent, or service principal with full traces.
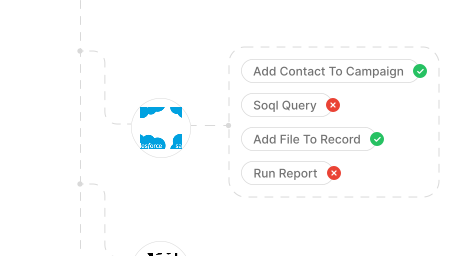
Per-tool authorization
Authorize different access levels for different types of tools by setting per-tool policies.
Secrets that don’t live on laptops
No local plaintext keys, no mystery config files. Enforce credential flows, handle rotation and revocation, and plug into your existing vault.
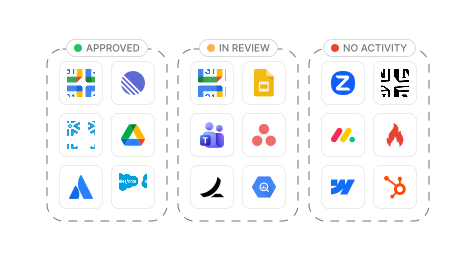
MCP inventory and auditing
See every MCP client and server, local or remote, in one place. Spot unauthorized MCPs before they become a risk.
Stay in control of AI across your company